


Anthropic Pledges 5% of Its Shares to a Public Benefit Fund. Governance Comes Later
Anthropic plans to put 5% of its shares into a public benefit fund. Here is how the stake can grow, what remains unclear, and why governance matters.

French Supermarket Fridge Hacks: Why a Factory Reset Is Not Enough
France’s refrigeration-controller attacks hit hundreds of supermarkets. Here is how to contain Danfoss and XWEB systems without inviting reinfection.

Copilot Studio Agents Get Microsoft 365 Accounts: What Admins Need to Know
Microsoft’s new Copilot Studio agent accounts add mailboxes, Teams presence and Entra identities. Here are the permissions, shared-memory risks and preview limits admins should check.

OpenCode Breach Exposed Provider API Keys: What Console Users Should Rotate
OpenCode says a breach affected 1.4% of Console users with external providers linked. Here is how to scope exposure, rotate AI API keys and audit usage.
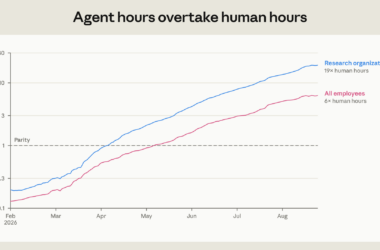
Anthropic Logs Six Agent-Hours per Employee Hour as Junior Hiring Shrinks
Anthropic’s internal study shows agent runtime at six times employee hours and junior technical hiring falling. The data also reveals a growing review bottleneck.
ConnectWise Cloud Backup Breach: Check These 7 Microsoft 365 App Identities
ConnectWise disabled seven cloud application identities after attackers entered Microsoft 365 tenants. Here is what MSPs should preserve, disable and inspect now.
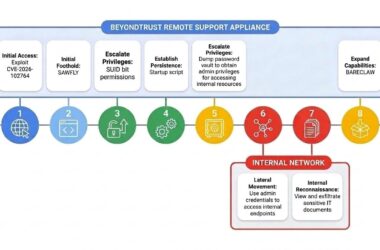
BeyondTrust Zero-Day Gave Attackers Root and Remote Sessions: What to Check
CVE-2026-102764 let attackers move from a PHP web shell to root, vault access and downstream Remote Support sessions. Here is the evidence and response order.
UK Regulator Targets Microsoft’s Copilot, Cloud Licensing and Security Bundles
The UK CMA could require Copilot API parity, rival AI defaults, unbundling and fairer cloud licensing if Microsoft receives strategic market status.
Meta Removed AI-Training Language From Its Terms. Crawling Permission Remains
Meta deleted the clearest AI-training clause from its October 30 business terms, but broad website-crawling permission remains. Here is what site owners should audit.
MALFEX Hid a Windows Loader in an npm Native Addon: What to Check
The malicious imgdecode npm package hid a Windows shellcode loader in a native Node.js addon. Here is how it evaded common checks and what defenders should inspect.