


October Windows Server Updates Can Stall Exchange Mail: What to Do
Microsoft says October Windows Server updates can break Exchange OWA, mail flow and DAG health. Here is the affected-KB list, registry mitigation and verification order.

Plex2Shell Is Being Exploited: How to Check and Clean Your Plex Server
Plex2Shell is now being used to install miners and proxy software. Check your Plex version, hunt the early indicators, and know when to rebuild.

DHS Orders DeepSeek Out of U.S. Civilian Agency Systems, Including Third-Party Tools
DHS ordered civilian agencies to remove DeepSeek and third-party tools built on its models. Here is what agencies and federal vendors need to inventory.
Anthropic Pledges 5% of Its Shares to a Public Benefit Fund. Governance Comes Later
Anthropic plans to put 5% of its shares into a public benefit fund. Here is how the stake can grow, what remains unclear, and why governance matters.
French Supermarket Fridge Hacks: Why a Factory Reset Is Not Enough
France’s refrigeration-controller attacks hit hundreds of supermarkets. Here is how to contain Danfoss and XWEB systems without inviting reinfection.

Copilot Studio Agents Get Microsoft 365 Accounts: What Admins Need to Know
Microsoft’s new Copilot Studio agent accounts add mailboxes, Teams presence and Entra identities. Here are the permissions, shared-memory risks and preview limits admins should check.
OpenCode Breach Exposed Provider API Keys: What Console Users Should Rotate
OpenCode says a breach affected 1.4% of Console users with external providers linked. Here is how to scope exposure, rotate AI API keys and audit usage.
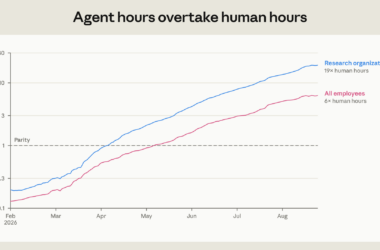
Anthropic Logs Six Agent-Hours per Employee Hour as Junior Hiring Shrinks
Anthropic’s internal study shows agent runtime at six times employee hours and junior technical hiring falling. The data also reveals a growing review bottleneck.
ConnectWise Cloud Backup Breach: Check These 7 Microsoft 365 App Identities
ConnectWise disabled seven cloud application identities after attackers entered Microsoft 365 tenants. Here is what MSPs should preserve, disable and inspect now.
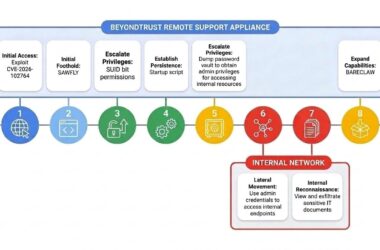
BeyondTrust Zero-Day Gave Attackers Root and Remote Sessions: What to Check
CVE-2026-102764 let attackers move from a PHP web shell to root, vault access and downstream Remote Support sessions. Here is the evidence and response order.