

Browsing Category
Networking
23 posts
Enterprise networking, data center fabrics, wireless and wired network operations, SASE, routing, switching, and the network infrastructure behind AI, cloud, security, and connected devices.

Check Point Zero-Day Puts Firewall Management Servers on a Three-Day Patch Clock
Check Point patched an exploited management-server zero-day and confirmed Spark VPN attacks. Here are the fixed hotfix takes, hunt commands, and September 25 deadline.

Cisco Email Gateway Zero-Day Turns Mail Security Into Incident Triage
Cisco has patched CVE-2026-76461, an actively exploited Secure Email Gateway SQL injection flaw that can let unauthenticated attackers run commands as root. Because CISA added it to the KEV catalog with a September 17 deadline, admins should treat patching as the start of incident triage, not the end.
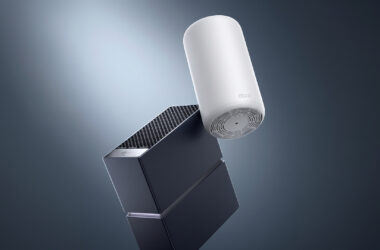
TP-Link’s Wi-Fi 8 Routers Make Reliability the Next Home-Network Pitch
TP-Link unveiled the Archer 8 Ultra router and Deco 8 Ultra mesh system at IFA 2026, putting early Wi-Fi 8 hardware on a preorder clock before the IEEE 802.11bn standard is final. The real upgrade pitch is not peak speed. It is fewer dead zones, smoother roaming, and more stable connections in crowded homes.
PaperCut Zero-Days Turn Print Servers Into Remote-Access Beachheads
PaperCut NG/MF customers face an actively exploited two-flaw chain that can turn exposed print-management servers into remote-access footholds. Admins should apply Emergency Patch Release 2, restrict web access, and check for pc-app.exe child processes, deleted logs, SimpleHelp, and AnyDesk activity.
Gunra Ransomware Puts VPN Gateways and Backups on the Same Incident List
A new FBI, CISA, NSA, Secret Service, DC3, and South Korean police advisory says Gunra ransomware affiliates are abusing exposed VPN and firewall paths, stealing cloud data, dumping credentials, and deleting backups before encryption. The useful response starts with edge-device patching, identity triage, immutable backups, and log review before recovery begins.
N-able N-central Hotfix Turns RMM Servers Into an Incident Response Drill
N-able has released a second required hotfix for an actively exploited N-central authentication-bypass flaw. For MSPs and enterprise IT teams, the work is not only upgrading to 2026.3.1.10, but also checking Take Control sessions, Cloudflare Tunnel persistence, and downstream endpoints before treating the RMM platform as trusted again.
Check Point SmartConsole Zero-Day Puts Firewall Management on Patch Deadline
Check Point has patched CVE-2026-16232, an actively exploited SmartConsole authentication bypass that can give attackers full administrator access to exposed Security Management servers. The urgent work is not only installing the Jumbo Hotfix, but also restricting Trusted Clients and checking management logs for signs of compromise.
Russian Router Campaign Turns SNMP Into a Critical Infrastructure Risk
NSA, CISA, the FBI, and 15 allied agencies warn that Russian FSB Center 16 actors are still compromising poorly configured routers across critical infrastructure. The practical fix starts with SNMPv3, blocked management protocols, patched firmware, and a hard look at exposed network devices.
New CitrixBleed Flaw Puts NetScaler SAML Gateways on Patch Watch
CVE-2026-8451 affects NetScaler ADC and Gateway appliances configured as SAML identity providers, and Lupovis says exploit payloads appeared within 24 hours of disclosure. Admins should verify SAML IdP exposure, upgrade affected builds, and review SAML endpoint logs before treating the issue as routine patching.
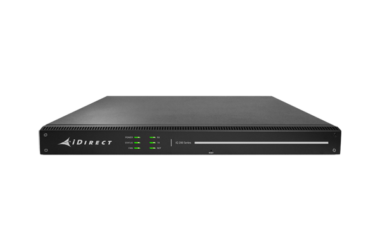
iDirect Satellite Terminal Flaws Put Link Management on the Patch List
CISA says ST Engineering iDirect iQ-Series satellite terminals running software 4.5.2.1 or earlier expose sensitive device identifiers and can be forced into reboots through weak API controls. Operators should treat the July 2 advisory as both a patch event and a management-plane exposure audit.