


Browsing Category
Enterprise Tech
146 posts
Enterprise software, IT operations platforms, business infrastructure, observability, SaaS, and workplace technology coverage.
Databricks Turns the Lakehouse Into an Operating Layer for AI Agents
Databricks used Data + AI Summit 2026 to launch Lakehouse//RT, Genie One, CustomerLake, Unity AI Gateway updates, and a Panther acquisition. The moves show the company trying to make the lakehouse a governed operating layer for real-time apps, agents, marketing, and security operations.

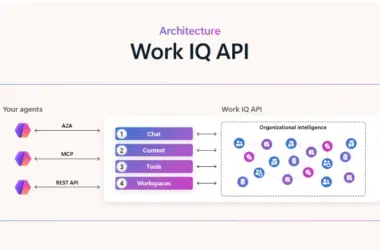
Microsoft Work IQ APIs Put Enterprise Agents Inside the Microsoft 365 Trust Boundary
Microsoft Work IQ APIs are generally available today, giving custom and third-party agents a governed way to use Microsoft 365 context, tools, workspaces, and Copilot-style responses. The real test is whether enterprises can manage permissions, audit trails, and Copilot Credits before agents start acting across work data.
Salesforce’s $3.6B Fin Deal Makes Customer-Service AI a CRM Battleground
Salesforce agreed to buy Fin, formerly Intercom, for about $3.6 billion. The deal gives Agentforce a faster-deploying customer-service AI agent and shows why CRM vendors are buying proven agent products, not just building broad platforms.
NewCore’s $66M Launch Puts AI Agents Inside the Identity Stack
NewCore emerged from stealth with $66 million and an identity-security platform built for AI agents. The launch shows why enterprises need agent identities, revocation paths, and access controls before autonomous tools touch production systems.
Oracle PeopleSoft Zero-Day Turns ERP Servers Into an Incident Response Priority
Oracle’s CVE-2026-35273 alert, CISA’s exploited-vulnerability listing, and Mandiant’s ShinyHunters findings make PeopleSoft patching only the first step. Exposed systems need log review, endpoint checks, and network hardening now.
Splunk Enterprise Flaw Hits CISA’s Exploited-Vulnerability List
CISA added CVE-2026-20253 to its Known Exploited Vulnerabilities catalog after evidence of active exploitation, and Splunk now says it is aware of limited exploitation. Affected self-managed Splunk Enterprise 10.0 and 10.2 systems should upgrade or carefully apply the PostgreSQL sidecar mitigation.