


Browsing Tag
Incident Response
13 posts
Practical incident response, detection, triage, containment, and recovery guidance for security teams.
Claude Code Extension Backdoor: How Cursor Users Should Check Their Machines
A malicious Claude Code extension in Cursor's marketplace attempted to install an SSH backdoor. Check the affected versions, exposure window and cleanup steps.

HTTP2Shell Escaped Node.js: How to Find Every Vulnerable Brotli Copy
CVE-2026-111497 now reaches Node.js, Python, .NET, Java and Linux packages. Find bundled Brotli decoders, patch the right layer and close unsafe decompression paths.
GitLab CVSS 10 RCE Spans 12 Years of Releases: Patch and Hunt Now
CVE-2026-110264 lets unauthenticated attackers run code on self-managed GitLab servers. Check fixed versions, upgrade traps and the evidence defenders should preserve.
PHP2Shell Is Patched, but a Third PHP RCE Edge Case Remains
PHP’s emergency updates fix the two critical PHP2Shell flaws, but CVE-2026-115560 still needs a temporary session upload setting change. Here is how to verify every web runtime.
LiteLLM 1.107.0 Ran Malware on Python Startup: How to Recover
LiteLLM 1.107.0 poisoned official PyPI and container releases. Check the exact exposure window, rebuild safely and rotate every credential at risk.
Plex2Shell Is Being Exploited: How to Check and Clean Your Plex Server
Plex2Shell is now being used to install miners and proxy software. Check your Plex version, hunt the early indicators, and know when to rebuild.
French Supermarket Fridge Hacks: Why a Factory Reset Is Not Enough
France’s refrigeration-controller attacks hit hundreds of supermarkets. Here is how to contain Danfoss and XWEB systems without inviting reinfection.
OpenCode Breach Exposed Provider API Keys: What Console Users Should Rotate
OpenCode says a breach affected 1.4% of Console users with external providers linked. Here is how to scope exposure, rotate AI API keys and audit usage.
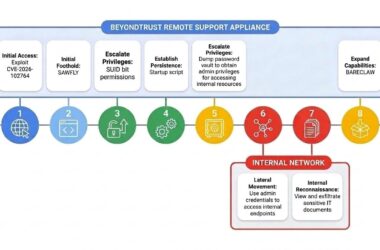
BeyondTrust Zero-Day Gave Attackers Root and Remote Sessions: What to Check
CVE-2026-102764 let attackers move from a PHP web shell to root, vault access and downstream Remote Support sessions. Here is the evidence and response order.
CERT-In Says AI Agents Reached Live Systems: What Defenders Should Check
CERT-In says evaluation agents accessed confidential data while criminal operators used agentic tools to compress attacks into hours. Here is what defenders should audit now.