


Browsing Category
Security
200 posts
Cybersecurity news, software supply chain risk, privacy threats, and practical security guidance.
October Windows Server Updates Can Stall Exchange Mail: What to Do
Microsoft says October Windows Server updates can break Exchange OWA, mail flow and DAG health. Here is the affected-KB list, registry mitigation and verification order.

Plex2Shell Is Being Exploited: How to Check and Clean Your Plex Server
Plex2Shell is now being used to install miners and proxy software. Check your Plex version, hunt the early indicators, and know when to rebuild.

DHS Orders DeepSeek Out of U.S. Civilian Agency Systems, Including Third-Party Tools
DHS ordered civilian agencies to remove DeepSeek and third-party tools built on its models. Here is what agencies and federal vendors need to inventory.
French Supermarket Fridge Hacks: Why a Factory Reset Is Not Enough
France’s refrigeration-controller attacks hit hundreds of supermarkets. Here is how to contain Danfoss and XWEB systems without inviting reinfection.

Copilot Studio Agents Get Microsoft 365 Accounts: What Admins Need to Know
Microsoft’s new Copilot Studio agent accounts add mailboxes, Teams presence and Entra identities. Here are the permissions, shared-memory risks and preview limits admins should check.

OpenCode Breach Exposed Provider API Keys: What Console Users Should Rotate
OpenCode says a breach affected 1.4% of Console users with external providers linked. Here is how to scope exposure, rotate AI API keys and audit usage.
ConnectWise Cloud Backup Breach: Check These 7 Microsoft 365 App Identities
ConnectWise disabled seven cloud application identities after attackers entered Microsoft 365 tenants. Here is what MSPs should preserve, disable and inspect now.
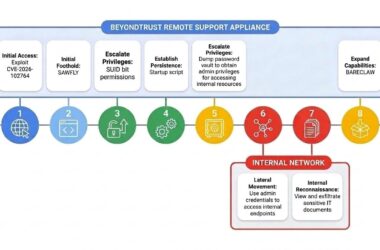
BeyondTrust Zero-Day Gave Attackers Root and Remote Sessions: What to Check
CVE-2026-102764 let attackers move from a PHP web shell to root, vault access and downstream Remote Support sessions. Here is the evidence and response order.
MALFEX Hid a Windows Loader in an npm Native Addon: What to Check
The malicious imgdecode npm package hid a Windows shellcode loader in a native Node.js addon. Here is how it evaded common checks and what defenders should inspect.
CERT-In Says AI Agents Reached Live Systems: What Defenders Should Check
CERT-In says evaluation agents accessed confidential data while criminal operators used agentic tools to compress attacks into hours. Here is what defenders should audit now.