


Browsing Category
How-to
94 posts
Step-by-step technology guides, practical tutorials, troubleshooting help, software tips, device setup, privacy guidance, and useful how-to coverage for everyday users.
Langflow Attacks Turn AI Workflow Servers Into Credential Targets
Attackers are actively exploiting Langflow flaws to pull OpenAI keys, AWS secrets, environment variables, and Langflow superuser credentials from exposed AI workflow servers. Teams running Langflow should treat patching as only the first step: credential rotation, log review, and network isolation matter just as much.

PaperCut Zero-Days Turn Print Servers Into Remote-Access Beachheads
PaperCut NG/MF customers face an actively exploited two-flaw chain that can turn exposed print-management servers into remote-access footholds. Admins should apply Emergency Patch Release 2, restrict web access, and check for pc-app.exe child processes, deleted logs, SimpleHelp, and AnyDesk activity.
OpenAI’s Assistants API Shutdown Puts Agent Apps on a Migration Clock
OpenAI’s Assistants API reaches its August 26, 2026 shutdown date today, forcing remaining beta-era agent apps toward the Responses API, Conversations, and dashboard-managed Prompts. Developers should treat the migration as an architecture change, not a search-and-replace endpoint swap.
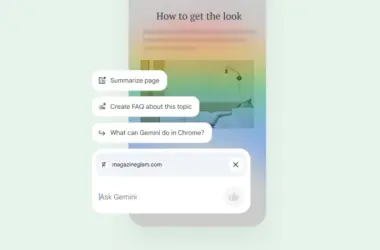
Gemini in Chrome Arrives on Android as Auto Browse Goes Mobile
Google made Gemini in Chrome available to all Android users in the U.S. on August 18, with page summaries, Google app connections, Nano Banana image tools, and paid auto browse support for AI Pro and Ultra subscribers. The useful change is mobile browser assistance; the risk is letting an agent act too close to accounts, purchases, and private page context.
ChatGPT for Teens Makes Age Checks a Default AI Safety Layer
OpenAI launched ChatGPT for Teens on August 18, automatically applying stricter safeguards, study-focused behavior, quiet hours, and optional parental controls for users ages 13 to 17. The useful shift is not just a family settings menu, but age assurance becoming a default layer for consumer AI.
Chrome’s 7 Billion-Notification Cleanup Turns Web Alerts Into a Security Setting
Google says Chrome reduced unwanted Android web notifications by more than 7 billion a day in the first quarter of 2026. The change is more than inbox cleanup: Chrome is treating notification permission as revocable trust, using Safety Hub, Safe Browsing, abuse-network detection, and server-side Push API throttling to cut off scam and malware campaigns.
Gunra Ransomware Puts VPN Gateways and Backups on the Same Incident List
A new FBI, CISA, NSA, Secret Service, DC3, and South Korean police advisory says Gunra ransomware affiliates are abusing exposed VPN and firewall paths, stealing cloud data, dumping credentials, and deleting backups before encryption. The useful response starts with edge-device patching, identity triage, immutable backups, and log review before recovery begins.
Microsoft’s August Patch Tuesday Makes AFD.sys the Patch Priority
Microsoft’s August 2026 Patch Tuesday fixes roughly 400 vulnerabilities, including an actively exploited AFD.sys privilege-escalation flaw. Windows teams should patch the exploited kernel bug first, then move quickly through exposed server roles, Office, SharePoint, and other high-risk systems.
N-able N-central Hotfix Turns RMM Servers Into an Incident Response Drill
N-able has released a second required hotfix for an actively exploited N-central authentication-bypass flaw. For MSPs and enterprise IT teams, the work is not only upgrading to 2026.3.1.10, but also checking Take Control sessions, Cloudflare Tunnel persistence, and downstream endpoints before treating the RMM platform as trusted again.