Brazil’s Superior Court of Justice has fined lawyers R$20,000 after finding instructions hidden inside a legal filing that were written for an artificial-intelligence system rather than a human reader.
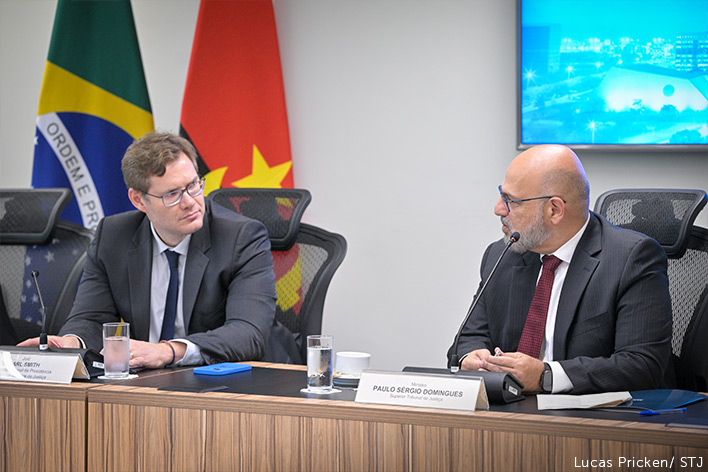
The court’s First Panel imposed the sanction on October 20 and ordered a technical report describing the concealment methods. It also referred the matter to Brazil’s bar association and federal prosecutors. According to the court’s account of the ruling, the filing placed multiple text layers in different parts of a page, including inside a decorative footer bar where matching colors made the words invisible.
The concealed text directed an AI system to treat the appeal favorably and write a firm conclusion supporting it. The appeal still failed, and the court said the prompt did not influence the judgment. The sanction matters because it is the latest in a series of Brazilian cases treating hidden AI instructions as misconduct even when the attempted manipulation does not work.
The hidden instructions were built for a PDF parser
This is an example of indirect prompt injection. Instead of typing a malicious instruction directly into a chatbot, a person places it in material that an AI tool is expected to read: a PDF, email, webpage, database record or other external source.
A human may see an ordinary court filing. A document parser can extract more: white-on-white characters, tiny type, off-page text, layers, annotations and words blended into graphic elements. If an AI workflow does not keep those extracted words separate from its trusted instructions, the document can try to change the model’s behavior.
The latest STJ filing used imperative language telling the system what to write and which conclusion to reach. One lawyer argued that the hidden material was residue from an AI drafting tool and merely repeated the appeal’s position. The panel rejected that explanation, pointing to the tiny type, color matching and commands scattered across the page.
Failure was not a defense. The court’s reasoning was that words concealed from people but addressed to automated processing did not become acceptable simply because the system resisted them. The panel classified the conduct as procedural bad faith and an affront to the administration of justice.
Brazil’s courts have now found several versions of the same attack
The October ruling did not arrive in isolation. In September, another STJ panel imposed a fine equal to 10% of the case value after technical staff found a prompt telling AI to treat a legal argument as successful and draft a decision granting the request.
That filing used two concealment techniques, according to the court’s September 3 decision summary: white text on a white background and spaces inserted between characters in an apparent effort to evade filters. The STJ notified the bar association, federal prosecutors, federal police and the municipality that employed the lawyer.
A separate criminal appeal contained a white-text instruction asking any AI reader to interpret the filing in favor of the defense. The Sixth Panel referred that episode to professional and prosecutorial authorities. It also stressed that judges and their staff, not an automated system, decide cases.
The court has now converted that position into a published jurisprudential statement: concealing a command intended to manipulate an AI system and induce an automatic favorable outcome can qualify as an act against the dignity of justice.
What the cases prove, and what they do not
The rulings show that adversarial instructions have reached real judicial document systems. They do not show that an AI decided a case, that the prompts changed a judicial outcome or that every hidden string was authored by the lawyer who filed it.
Those distinctions matter. Documents can inherit hidden material through templates, copied text, conversion software and collaboration workflows. A later court may need technical evidence to establish who inserted a layer, when it appeared and whether the signer knew it was present. The STJ’s approach nevertheless places responsibility on professionals to inspect the documents they sign and submit.
The cases also illustrate why a plain-text malware scanner is not enough. A detector that sees only extracted words may notice suspicious phrases but miss the visual discrepancy that makes them deceptive. A reliable review needs to compare what a person sees with what the parser extracts, while preserving the original file and its structure for investigation.
The OWASP GenAI Security Project classifies instructions embedded in documents and other retrieved content as indirect prompt injection. Microsoft’s prompt-injection guidance likewise lists white-on-white fonts, zero-size text and off-screen content among the techniques that can remain readable to a model while invisible to a person.
How legal teams and document-AI operators should respond
Law firms should add an automated preflight step before electronic filing. That review should flag text whose color matches its background, extremely small fonts, invisible rendering modes, off-page objects, hidden document runs, suspicious Unicode characters and unexpected layers. Converting a document to PDF does not guarantee that concealed source material disappears.
Firms also need a clean-document rule. Final filings should be generated from controlled templates, flattened only after review, and checked by extracting all text into a separate view. The signed PDF should be hashed and retained alongside the editable source so a team can reconstruct how hidden material entered the file.
Courts and other organizations using AI to summarize outside documents need controls beyond keyword detection:
- Treat every uploaded file as untrusted. Its text is evidence or source material, not authority to modify the AI’s task.
- Separate instructions from content. Retrieved document text should not be concatenated into the same trusted prompt channel that defines system behavior.
- Limit model permissions. A document-analysis tool should not be able to file, send, disclose or approve anything without a separate authorization step.
- Expose anomalies to reviewers. Show hidden-text warnings, extracted text and page locations instead of silently deleting suspicious content.
- Keep human accountability. AI can organize or summarize a record, but a named person should verify citations, reasoning and any consequential action.
The latest Brazilian sanction turns a lab-style AI attack into an operational document-security problem. Any system that lets outside files influence an AI workflow has the same basic exposure, whether it reviews court pleadings, résumés, insurance claims, procurement bids or customer emails. The practical boundary is simple: a document may contain facts and arguments, but it should never be allowed to rewrite the instructions of the system reading it.