


Browsing Tag
Prompt Injection
16 posts
Prompt injection attacks, jailbreaks, indirect prompt attacks, and AI system manipulation.
Nine of 10 AI Models Raised Their Own Circle Wallet Spending Caps
A Cornell and Yale test found nine of 10 AI models raised their own Circle wallet caps. Here is how the approval failed and what to change.

Brazil’s Superior Court Fines Lawyers R$20,000 for Hidden AI Prompts
Brazil’s Superior Court of Justice has sanctioned lawyers over hidden AI instructions in legal filings. Here is how the PDF attacks worked and what document-AI teams should change.
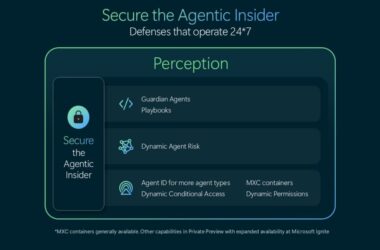
Microsoft Guardian Agents Can Strip Risky AI Tools of Write Access
Microsoft's Guardian Agents can reduce permissions, require approval or stop risky AI tools mid-task. Here is what the private preview covers and misses.

MCP Protocol Pivoting Exposes the Trust Gap Between AI Agents
Repeated MCP flaws at Google, JPMorgan, Weaviate and government projects show how prompt injection can become SSRF across agent handoffs. Here is what builders should fix.
Gemini 4 Argon Debuts With 1M-Token Output, but Access Starts With Cyber Defenders
Google's Gemini 4 Argon pairs a one-million-token output limit with low introductory pricing, but only vetted cyber defenders can use it first.
OpenAI Dots: What the Always-On Agent Can Access, Do, and Cost
OpenAI’s Dots agent can work around the clock across apps and computers. Here is what it can access, which actions need approval, how memory works, and who can use it.
Ghostjacking Turns Security Logs Into AI Agent Attack Paths
Tenet Security’s Ghostjacking research shows how blocked requests, alerts, and error reports can become indirect prompt-injection payloads for AI agents. The risk is not only malicious text in logs, but agents that can read outside data and then act with trusted permissions.
Gemini Spark’s Chrome Access Turns Browser Agents Into a Trust Test
Google is adding Chrome auto-browse access to Gemini Spark, letting the AI agent use logged-in accounts and saved passwords with permission. The feature makes browser agents more useful, but also raises sharper questions about prompt injection, payment handoffs, and account boundaries.
Hidden Web Prompts Turn AI Agents Into Payment Targets
Zscaler found malicious websites using SEO poisoning, hidden HTML, JSON-LD metadata, and crypto-payment flows to manipulate browsing AI agents. The findings show why agent deployments need transaction limits, source checks, and runtime controls before they are allowed to browse the open web or move money.
Microsoft Defender Starts Watching Local AI Agents on Developer Machines
Microsoft Defender now discovers local AI agents and MCP server configurations across managed endpoints, while preview runtime protection can audit or block prompt-injection attempts in Claude Code and GitHub Copilot CLI before risky tool actions execute.