


Browsing Tag
Microsoft
25 posts
Microsoft software, cloud, Windows, security, and platform coverage.

Microsoft Maia 300: Specs, 2027 Rollout, and What the Claims Mean
Microsoft’s Maia 300 packs eight HBM4 stacks into a 950W accelerator and 96 chips into a 167kW rack. Here’s what its 2027 rollout means.

Surface Laptop Ultra Starts at $2,599, but Battery Life Is Still the Big Unknown
Microsoft’s RTX Spark Surface Laptop Ultra can run 120B-parameter AI models locally, but its $2,599 price, Arm compatibility and undisclosed battery life deserve scrutiny.
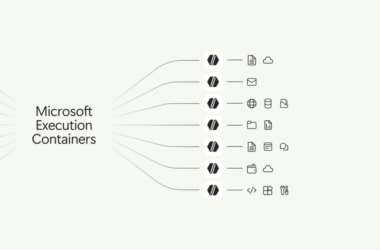
Microsoft Execution Containers Put AI Agents Behind OS-Enforced Boundaries
Microsoft Execution Containers are now generally available, with file, network, UI and session controls for AI agents. Here is how MXC works and what IT teams should test.
EvilTokens Disruption Exposes the Device-Code Phishing Gap
Microsoft and partners disrupted EvilTokens after more than 12,000 inbox compromises. Here is how device-code phishing bypasses normal expectations and what Microsoft 365 teams should change now.
Microsoft’s School AI Privacy Standard Turns Guardrails Into Contract Terms
Microsoft, the American Federation of Teachers, and the United Federation of Teachers have created a school AI privacy standard that districts can add to Microsoft agreements starting November 1. The important shift is not another AI pledge, but contract terms covering student data, model training, memory, agentic features, audits, and human oversight.
Microsoft’s August Patch Tuesday Makes AFD.sys the Patch Priority
Microsoft’s August 2026 Patch Tuesday fixes roughly 400 vulnerabilities, including an actively exploited AFD.sys privilege-escalation flaw. Windows teams should patch the exploited kernel bug first, then move quickly through exposed server roles, Office, SharePoint, and other high-risk systems.
Microsoft Project Perception Puts AI Agents on the Security Patch Path
Microsoft’s Project Perception enters public preview August 3 with MAI-Cyber-1-Flash inside MDASH, promising lower-cost vulnerability discovery and agentic security workflows. The important question is how much action enterprises should let AI security agents take.
SharePoint’s New Exploited RCE Turns Patching Into Key Rotation Triage
CISA added Microsoft SharePoint Server CVE-2026-58644 to its exploited-vulnerabilities catalog on July 16, two days after Microsoft patched it. Admins should patch, verify AMSI, hunt for machine-key theft, and reduce internet exposure before treating the farm as clean.
Microsoft Purview Migration Puts Defender DLP Policies on a Deadline
Microsoft is retiring Defender for Cloud Apps file policies on January 6, 2027, forcing Microsoft 365 security teams to rebuild DLP and auto-labeling controls in Purview before existing policies stop being supported or enforced.
Microsoft Says AI Will Make Windows Security Updates Bigger
Microsoft says AI-assisted vulnerability discovery will increase the number of Windows security fixes customers see in each release. For IT teams, the shift makes patch operations less about one monthly event and more about continuous risk-based deployment.