

Browsing Tag
Enterprise Security
31 posts
Security issues affecting enterprise software, IT systems, identity, observability, and business infrastructure.
Zoom’s Windows Account-Takeover Bug Makes Client Updates an Admin Priority
Zoom has patched CVE-2026-53412, a critical Windows client flaw that could let an unauthenticated attacker take over accounts over the network. The practical response is to verify Zoom Workplace and VDI client versions, not just assume auto-update has reached every endpoint.


SharePoint’s New Exploited RCE Turns Patching Into Key Rotation Triage
CISA added Microsoft SharePoint Server CVE-2026-58644 to its exploited-vulnerabilities catalog on July 16, two days after Microsoft patched it. Admins should patch, verify AMSI, hunt for machine-key theft, and reduce internet exposure before treating the farm as clean.
Microsoft Purview Migration Puts Defender DLP Policies on a Deadline
Microsoft is retiring Defender for Cloud Apps file policies on January 6, 2027, forcing Microsoft 365 security teams to rebuild DLP and auto-labeling controls in Purview before existing policies stop being supported or enforced.
New CitrixBleed Flaw Puts NetScaler SAML Gateways on Patch Watch
CVE-2026-8451 affects NetScaler ADC and Gateway appliances configured as SAML identity providers, and Lupovis says exploit payloads appeared within 24 hours of disclosure. Admins should verify SAML IdP exposure, upgrade affected builds, and review SAML endpoint logs before treating the issue as routine patching.
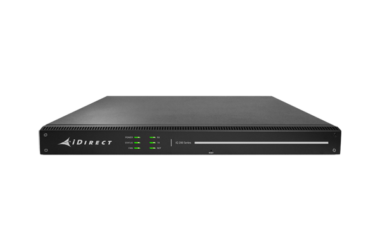
iDirect Satellite Terminal Flaws Put Link Management on the Patch List
CISA says ST Engineering iDirect iQ-Series satellite terminals running software 4.5.2.1 or earlier expose sensitive device identifiers and can be forced into reboots through weak API controls. Operators should treat the July 2 advisory as both a patch event and a management-plane exposure audit.
Adobe ColdFusion Exploitation Turns Patch Into Incident Triage
CVE-2026-48282 is now being exploited against Adobe ColdFusion, turning Adobe's June 30 patch from routine maintenance into incident triage. Admins should update ColdFusion 2025 and 2023, review logs from the disclosure window, and verify exposed paths are closed.
Cisco’s Twice-Monthly Patch Cadence Starts With Catalyst Center and ClamAV Fixes
Cisco’s first July security-advisory drop under its new twice-monthly cadence includes a Catalyst Center arbitrary-file-read flaw and seven ClamAV vulnerabilities affecting Cisco Secure Endpoint. The change gives network and security teams more predictability, but it also means Cisco infrastructure patch planning needs to become a standing operating rhythm, not a quarterly scramble.
SharePoint RCE Gives Admins a July 4 Patch Deadline
CISA has added Microsoft SharePoint Server CVE-2026-45659 to its exploited-vulnerabilities catalog, giving federal agencies until July 4 to apply mitigations and run forensic triage. The flaw was patched in May, but active exploitation means on-prem SharePoint teams should verify builds, review exposure, and check for compromise now.
BlueHammer Ransomware Flag Puts Microsoft Defender Patching Back on the Clock
CISA has updated the Microsoft Defender BlueHammer flaw, CVE-2026-33825, to mark it as used in ransomware campaigns. The flaw was patched in April, but the new flag gives Windows teams a fresh reason to verify Defender updates, endpoint telemetry, and local privilege escalation controls.
SimpleHelp Exploit Turns Remote Support Into a Credential Theft Pipeline
Attackers are exploiting CVE-2026-48558 in SimpleHelp to turn remote support access into a malware delivery path. Teams should patch, hunt for forged technician sessions, and rotate credentials exposed on managed endpoints.