


Browsing Category
Developer Tools
111 posts
Developer tools, coding workflows, package managers, software engineering platforms, cloud development environments, AI coding assistants, language tooling, and developer productivity news.
Meta Runs Google TPUs in Production as TorchTPU Opens the Stack
Meta is serving production AI workloads on Google TPUs through TorchTPU. Here is what the PyTorch-native stack supports, where it remains uneven, and what teams should test.

GitLab CVSS 10 RCE Spans 12 Years of Releases: Patch and Hunt Now
CVE-2026-110264 lets unauthenticated attackers run code on self-managed GitLab servers. Check fixed versions, upgrade traps and the evidence defenders should preserve.
PHP2Shell Is Patched, but a Third PHP RCE Edge Case Remains
PHP’s emergency updates fix the two critical PHP2Shell flaws, but CVE-2026-115560 still needs a temporary session upload setting change. Here is how to verify every web runtime.
LiteLLM 1.107.0 Ran Malware on Python Startup: How to Recover
LiteLLM 1.107.0 poisoned official PyPI and container releases. Check the exact exposure window, rebuild safely and rotate every credential at risk.
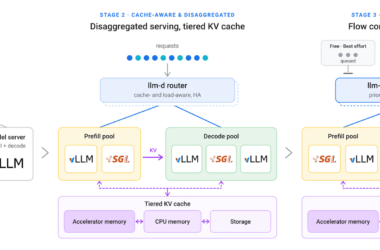
llm-d 1.0 Brings Agent-Aware Routing to Kubernetes AI Inference
llm-d 1.0 stabilizes APIs, adds agent-aware routing and coordinates zero-downtime inference upgrades. Here is what platform teams should test before migrating.
ReactOS Can Install on NTFS, but It Is Still an Alpha Test
ReactOS can finally install and boot on NTFS, but caching, journaling and security support are missing. Here is what changed and how to test it safely.
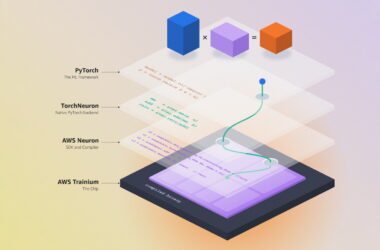
TorchNeuron Runs PyTorch on Trainium, but Beta Gaps Matter
Amazon's TorchNeuron makes Trainium a native PyTorch device. Here are the public beta's compatibility gaps, performance claims and migration checks.
OpenCode Breach Exposed Provider API Keys: What Console Users Should Rotate
OpenCode says a breach affected 1.4% of Console users with external providers linked. Here is how to scope exposure, rotate AI API keys and audit usage.
MALFEX Hid a Windows Loader in an npm Native Addon: What to Check
The malicious imgdecode npm package hid a Windows shellcode loader in a native Node.js addon. Here is how it evaded common checks and what defenders should inspect.
Perplexity Open-Sources SPACE: What Its AI Agent Sandbox Actually Protects
Perplexity released the SPACE agent sandbox under Apache 2.0. Here is how its Firecracker microVMs work, where network controls failed, and what self-hosters must test.