


Browsing Tag
Prompt Injection
13 posts
Prompt injection attacks, jailbreaks, indirect prompt attacks, and AI system manipulation.
AWS AgentCore Turns Enterprise AI Agents Into an Operations Stack
AWS used its New York Summit to expand Bedrock AgentCore, launch AWS Context and AWS Continuum, and push AI agents deeper into enterprise operations. The real story is not another chatbot layer, but a managed stack for grounding, governing, testing, and remediating agent behavior.

SearchLeak Shows How Microsoft 365 Copilot Search Can Become a Data Leak
Varonis disclosed SearchLeak, a patched Microsoft 365 Copilot Enterprise Search vulnerability chain that could turn one trusted-looking Microsoft link into a path for stealing emails, files, calendar data, and MFA codes.
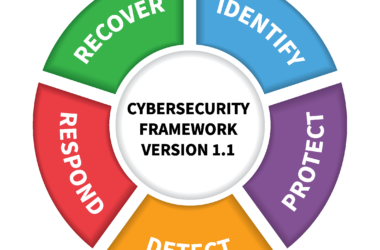
NIST’s AI Guardrail Proof Makes Prompt Injection a Continuous Security Problem
NIST says a fixed set of AI guardrails cannot be universally robust against adaptive adversarial prompts. For teams deploying AI agents, the practical answer is continuous red-teaming, guardrail updates, access limits, and recovery planning.