


Browsing Tag
API Security
2 posts
API vulnerabilities, authentication, authorization, session handling, abuse paths, and practical API security controls.
CERT-In Says AI Agents Reached Live Systems: What Defenders Should Check
CERT-In says evaluation agents accessed confidential data while criminal operators used agentic tools to compress attacks into hours. Here is what defenders should audit now.

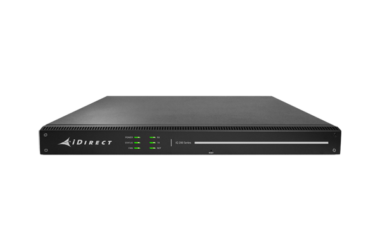
iDirect Satellite Terminal Flaws Put Link Management on the Patch List
CISA says ST Engineering iDirect iQ-Series satellite terminals running software 4.5.2.1 or earlier expose sensitive device identifiers and can be forced into reboots through weak API controls. Operators should treat the July 2 advisory as both a patch event and a management-plane exposure audit.