


Browsing Category
Security
137 posts
Cybersecurity news, software supply chain risk, privacy threats, and practical security guidance.
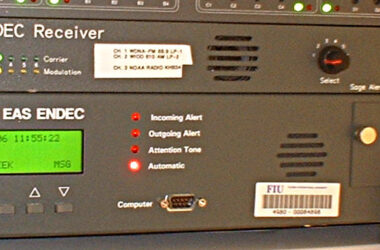
FCC Turns Emergency Alert Cybersecurity Into a Baseline Requirement
The FCC adopted targeted cybersecurity rules for Emergency Alert System participants after years of warnings about default passwords, unpatched gear, and internet-exposed alerting equipment. Broadcasters and cable operators will have 60 days after Federal Register publication to meet the new baseline.

Anthropic’s Mythos Test Shows Why AI Cyber Defense Is Becoming Classified Work
An Anthropic Mythos test with U.S. intelligence agencies reportedly found vulnerabilities in highly sensitive government systems within hours. The episode sharpens the policy problem around frontier AI: the same models that can help defenders fix critical software can also compress the timeline for attackers.
OpenAI Launches GPT-5.6 Sol Under Government-Restricted Preview
OpenAI has launched GPT-5.6 Sol, Terra, and Luna in a restricted preview after U.S. government review. The release brings new pricing, API and Codex access limits, stronger cyber safeguards, and a clearer look at how frontier model launches are becoming governed deployments.
curl 8.21.0 Fixes 25-Year-Old libcurl mTLS Bug
curl 8.21.0 fixes 18 security flaws, including CVE-2026-8932, a 25-year-old libcurl mTLS connection-reuse bug. The practical risk is in applications that embed libcurl and change client certificate settings while reusing connection pools.
Citizen Lab Says Russia Used Cellebrite on Activist’s iPhone After Cutoff
Citizen Lab says Russian authorities used Cellebrite forensic tools on activist Andrey Pivovarov’s iPhone months after Cellebrite said it had stopped selling to Russia and Belarus. The case turns phone forensics into a control problem: what happens when extraction tools keep working after a vendor cuts off a customer?
Mandiant Details Cisco SD-WAN Attack That Turned a Malicious CSV Into Root Access
Mandiant says an attacker used rogue Cisco Catalyst SD-WAN peering, admin password manipulation, and CVE-2026-20245 to gain root access through a malicious CSV upload. The new details make the June SD-WAN advisories an incident-response problem, not just a patching task.
Microsoft’s StealC and Amadey Takedown Hits the Credential-Theft Supply Chain
Microsoft, Europol, and security partners disrupted infrastructure used by StealC and Amadey, two malware-as-a-service tools tied to credential theft, ransomware access, and financial fraud. The operation matters because it targeted the supply chain behind intrusions, not just one malware family.
Dragos EmberAI Puts AI Security Workflows Inside the Control Room
Dragos launched EmberAI, an OT-native AI assistant for industrial cybersecurity teams. The product matters because critical infrastructure defenders need AI that understands plant assets, threat groups, vulnerable equipment, and operational impact rather than treating OT security like ordinary IT alert triage.
Meta Pauses Employee-Tracking Program After AI Training Data Exposure
Meta paused its Model Capability Initiative after reports that employee activity data collected for AI training was exposed internally. The episode shows why training AI agents on real workplace behavior needs security controls as strict as the systems those agents may eventually operate.
CISA Gives UniFi OS and Lantronix Flaws a June 26 Patch Deadline
CISA added three Ubiquiti UniFi OS flaws and a Lantronix EDS5000 code-injection bug to its Known Exploited Vulnerabilities catalog, setting a June 26 remediation deadline for federal agencies. The risk is not just another CVE list: exposed network management interfaces can become a fast path to device control.