

Browsing Category
Networking
23 posts
Enterprise networking, data center fabrics, wireless and wired network operations, SASE, routing, switching, and the network infrastructure behind AI, cloud, security, and connected devices.

Cisco’s Twice-Monthly Patch Cadence Starts With Catalyst Center and ClamAV Fixes
Cisco’s first July security-advisory drop under its new twice-monthly cadence includes a Catalyst Center arbitrary-file-read flaw and seven ClamAV vulnerabilities affecting Cisco Secure Endpoint. The change gives network and security teams more predictability, but it also means Cisco infrastructure patch planning needs to become a standing operating rhythm, not a quarterly scramble.

Daktronics Controller Flaws Put Public Digital Signs on Patch Watch
CISA is warning that flaws in Daktronics DMP-5000, VFC-DMP-5000, and DMP-8000 controller firmware could expose public display systems to root-level compromise. Operators of billboards, highway signs, venues, hospitals, and other connected displays should patch firmware, change default credentials, and verify that controllers are not reachable from the open internet.
SimpleHelp Exploit Turns Remote Support Into a Credential Theft Pipeline
Attackers are exploiting CVE-2026-48558 in SimpleHelp to turn remote support access into a malware delivery path. Teams should patch, hunt for forged technician sessions, and rotate credentials exposed on managed endpoints.
Cisco Unified CM Exploit Gives Voice Servers a June 28 Patch Deadline
CISA gave federal agencies until June 28 to fix CVE-2026-20230, a Cisco Unified Communications Manager SSRF flaw that can write files and lead to root access when WebDialer is enabled. Enterprise teams should treat it as a voice-infrastructure exposure check, not just another Cisco patch.
FCC Turns Emergency Alert Cybersecurity Into a Baseline Requirement
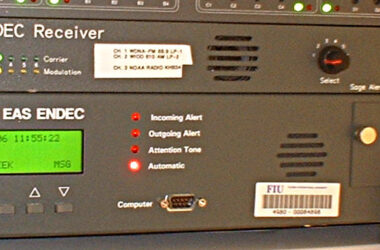
The FCC adopted targeted cybersecurity rules for Emergency Alert System participants after years of warnings about default passwords, unpatched gear, and internet-exposed alerting equipment. Broadcasters and cable operators will have 60 days after Federal Register publication to meet the new baseline.
Mandiant Details Cisco SD-WAN Attack That Turned a Malicious CSV Into Root Access
Mandiant says an attacker used rogue Cisco Catalyst SD-WAN peering, admin password manipulation, and CVE-2026-20245 to gain root access through a malicious CSV upload. The new details make the June SD-WAN advisories an incident-response problem, not just a patching task.
CISA Gives UniFi OS and Lantronix Flaws a June 26 Patch Deadline
CISA added three Ubiquiti UniFi OS flaws and a Lantronix EDS5000 code-injection bug to its Known Exploited Vulnerabilities catalog, setting a June 26 remediation deadline for federal agencies. The risk is not just another CVE list: exposed network management interfaces can become a fast path to device control.
CISA’s June 23 Deadline Puts Cisco SD-WAN, Chrome, and Arista EOS on the Triage List
CISA’s June 23 remediation deadline covers three actively exploited flaws across Cisco Catalyst SD-WAN Manager, Google Chrome’s V8 engine, and Arista EOS. The useful move for security teams is not treating them as one patch chore, but triaging each layer: network control plane, browsers, and tunnel decapsulation paths.
CISA Puts FortiSandbox Exploits on an Emergency Patch Clock
CISA added two Fortinet FortiSandbox command-injection flaws to its exploited-vulnerabilities catalog on July 16, giving federal agencies until July 19 to remediate. Security teams should patch affected FortiSandbox systems, restrict management access, and review logs and connected credentials if exposure existed before the upgrade.
AryStinger Botnet Turns Old Routers Into Attack Proxies
Security researchers say AryStinger has compromised more than 4,300 legacy routers, turning aging home and small-office gear into proxy and reconnaissance infrastructure. The campaign is a reminder that end-of-life routers are not just slow or outdated; they can become someone else’s attack platform.